
advertisement
Immaculate Kassait’s Tenure At ODPC: Milestones, Lessons And The Road Ahead

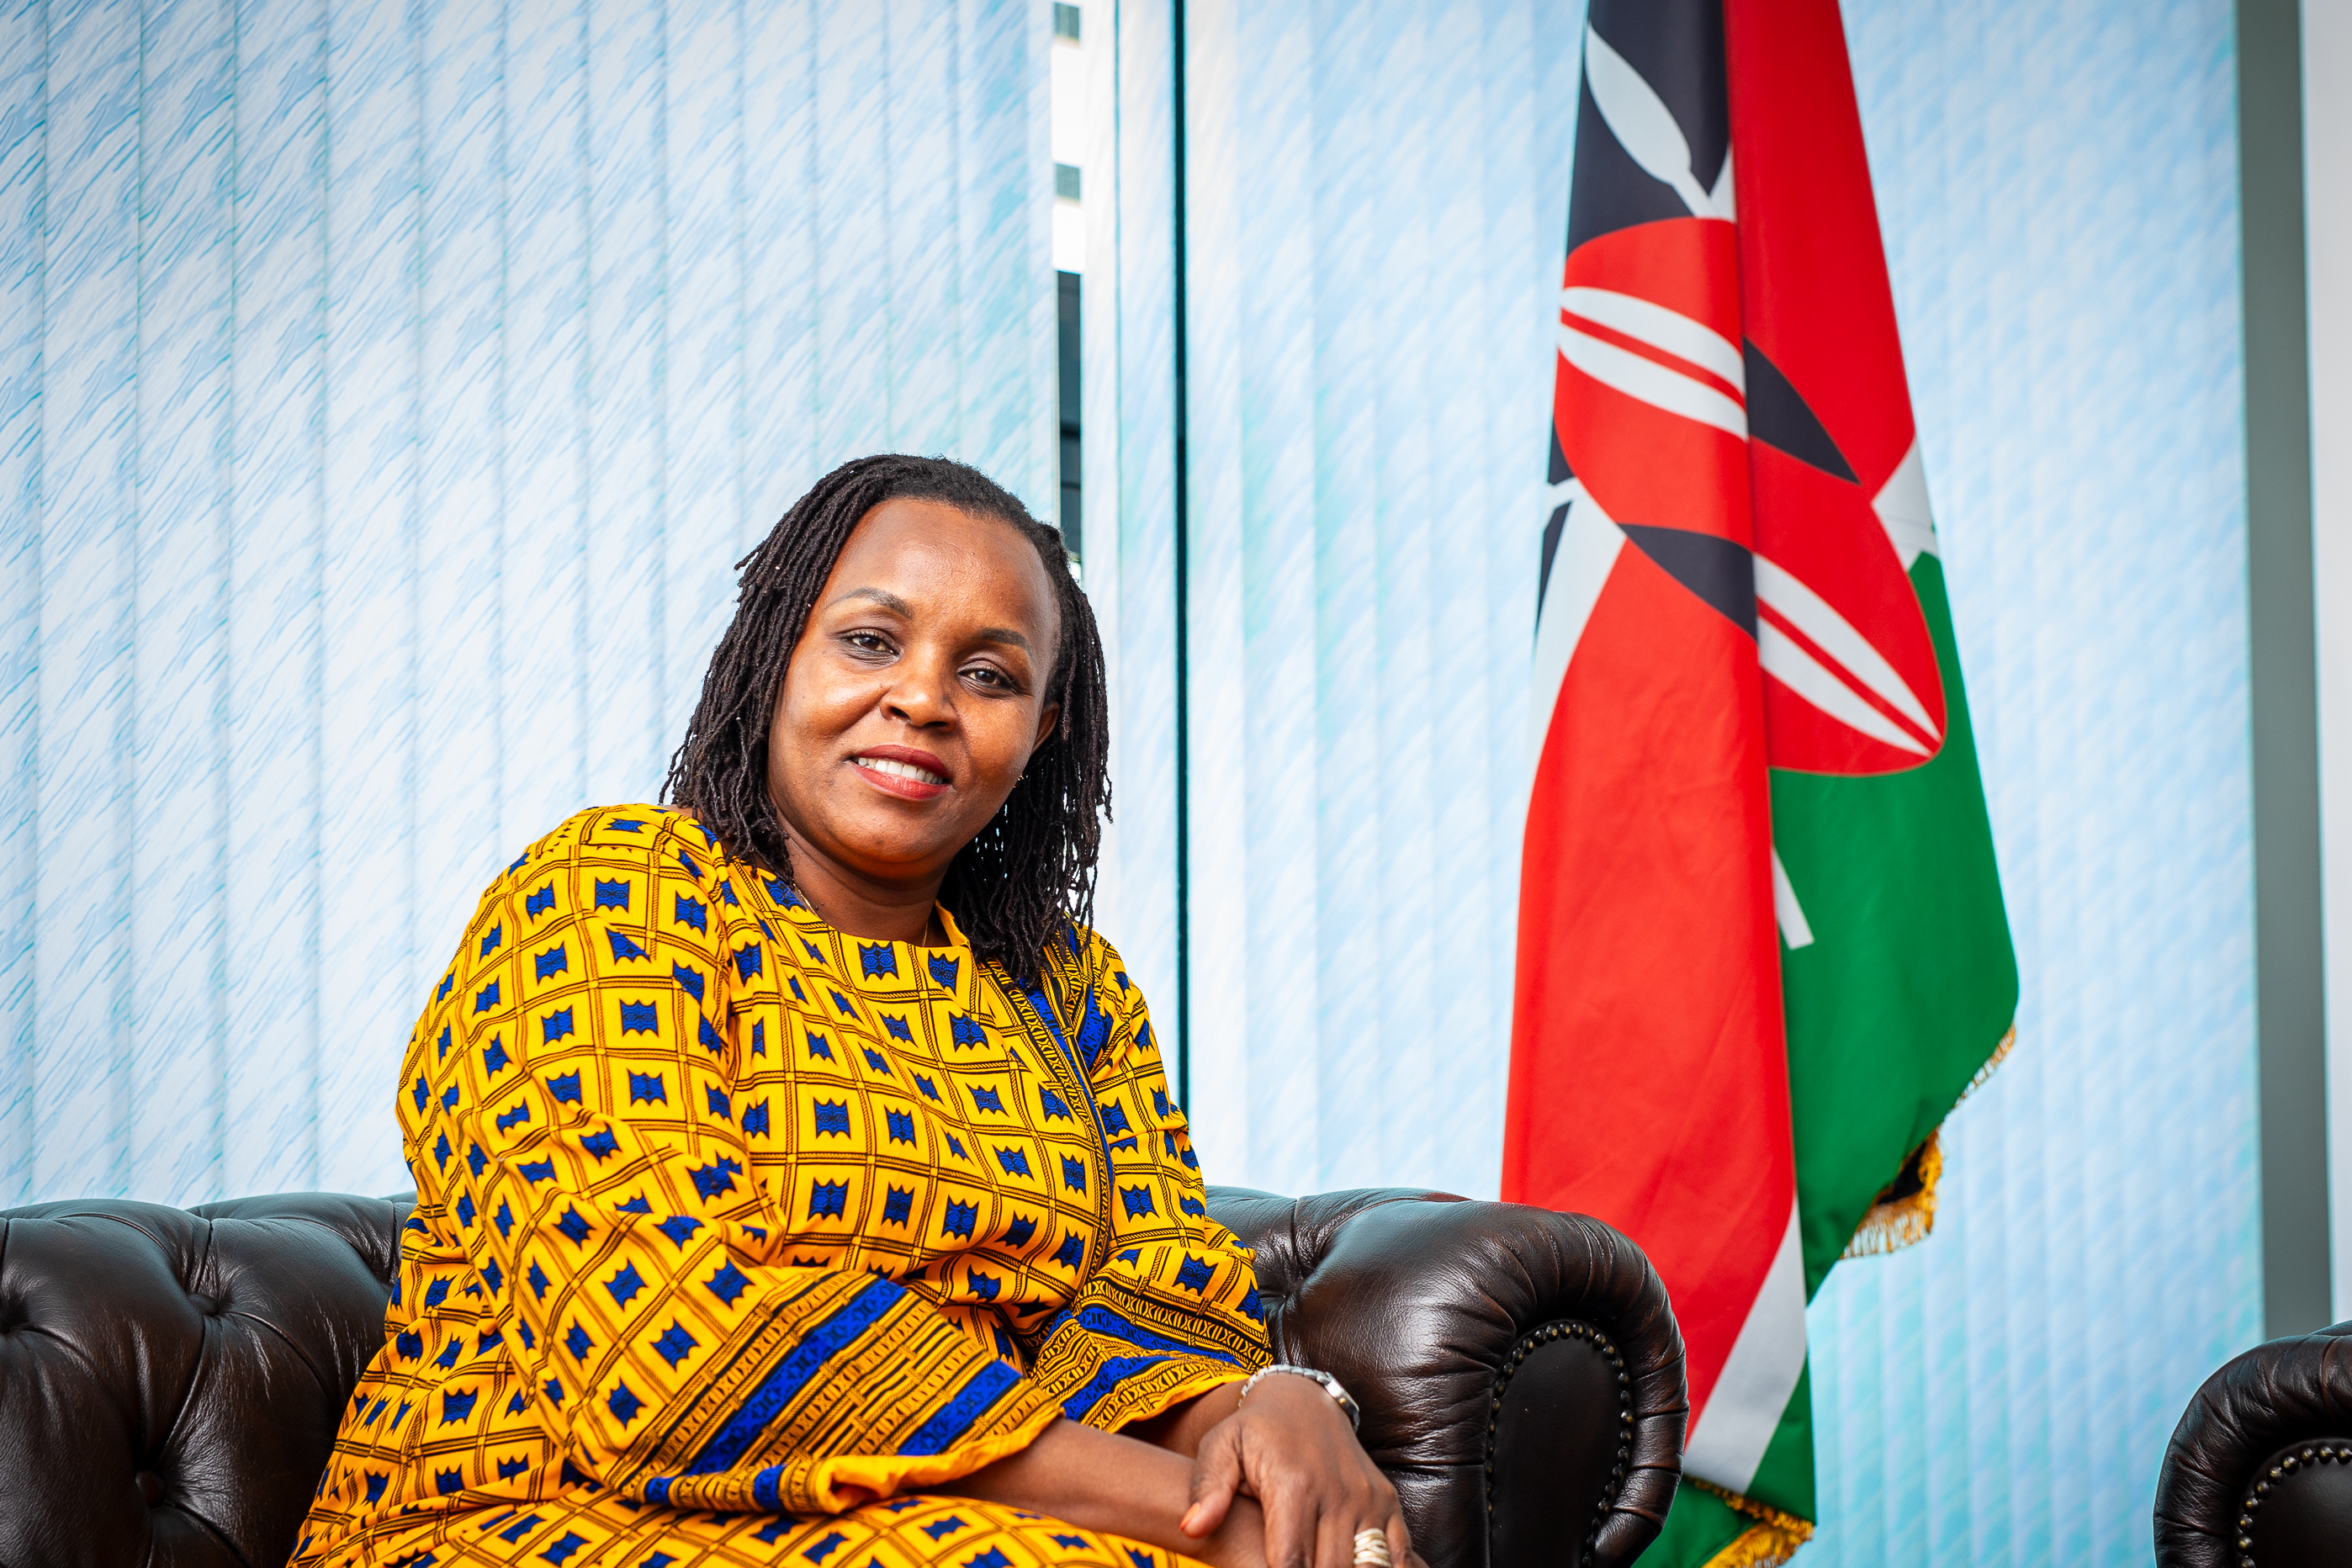
When Immaculate Kassait walked into the Office of the Data Protection Commissioner (ODPC) in November 2020, she was not taking over an established regulator. She was helping build one.
The Office had a mandate under Kenya’s data protection framework, but lacked many of the institutional structures, systems, processes and public awareness mechanisms needed to turn that mandate into a functioning regulatory institution.
Kassait’s tenure has coincided with a fundamental shift in how Kenya approaches personal data. Data protection has moved from a relatively new regulatory concept to a growing part of corporate governance, public-sector administration, technology policy and individual awareness.
advertisement
As she reflects on her tenure, Kassait discusses the challenges of establishing the ODPC, the evolution of enforcement, the rise of AI and digital public infrastructure, and the unfinished work facing her successor.
What did you find when you walked into the ODPC?
I was essentially walking into an institution that had a mandate but no institutional structures, systems, processes or public understanding and awareness.
advertisement
It was a big opportunity, but also an enormous responsibility. We had to establish an institution that Kenyans could trust while helping organisations understand what data protection meant in practical terms.
We were not simply implementing a law. We were building a new regulatory culture around privacy and the responsible use of personal data.
What did you have to build that did not exist before?
advertisement
Almost everything that makes a regulator function.
That included institutional structures, regulatory processes and policies, systems for handling complaints and registrations, investigative and enforcement capabilities, public awareness programmes and relationships with stakeholders.
The priorities were quite foundational: establishing the institution, putting the right people and systems in place, creating awareness about the new law and beginning to build public and stakeholder confidence in the Office.
What was the biggest challenge in establishing a new regulator, and how did you navigate it?
The biggest challenge was building credibility while building the institution itself.
As a new regulator, we had to establish our authority, but we also had to demonstrate that our authority was being exercised fairly, independently and in the public interest.
We were also introducing a relatively new concept to organisations across very different sectors. That meant engaging government, private companies, civil society, technology companies, professionals and ordinary citizens, all of whom had different levels of understanding of data protection.
We navigated this through a combination of education, engagement, guidance and, where necessary, enforcement.
Regulation is most effective when people understand both what is expected of them and why it matters.
When you accepted the appointment in 2020, what did you expect the ODPC to look like by the end of your tenure? How different is the reality?
I expected the ODPC to become a credible, independent and respected regulator capable of protecting the rights of data subjects while supporting responsible innovation.
The Office has grown institutionally, our enforcement work has become more visible, public awareness has increased, and data protection has become part of conversations around business, government and technology.
Today, organisations and citizens are much more likely to ask questions about how personal data is collected, used, shared and protected. That shift in consciousness is significant.
Five to six years later, how would you describe the transformation of Kenya’s data protection landscape?
Years ago, data protection was largely a new regulatory concept for many organisations. Today, it has become part of corporate governance, public-sector administration, technology conversations and individual awareness.
We have moved from introducing the framework to operationalising it. Organisations are increasingly appointing data protection officers, conducting assessments, reviewing their data practices and engaging with the regulator.
Citizens are also becoming more conscious of their rights. They are asking questions, raising complaints and expecting organisations to account for how their personal information is handled.
What is the single biggest change you have seen in how Kenyan organisations handle personal data?
Organisations are increasingly recognising that personal data is not simply an asset that they collect and store. It is information entrusted to them, and that comes with responsibility.
Organisations now think more carefully about why they need particular information, how long they should retain it, who should have access to it and what safeguards should be in place.
The conversation has definitely moved from, “Do I have to comply?” to, “How do I build responsible data practices into the way my organisation operates?”
Has Kenya moved from treating data protection primarily as a compliance requirement to recognising it as a fundamental business and governance issue?
Yes.
Compliance remains important because organisations need to meet the requirements of the law. But increasingly, organisations are recognising that good data governance is also good business and good governance.
Data sits at the centre of almost every modern organisation. If managed responsibly, you build trust. If you misuse it or fail to protect it, you damage your reputation, expose people to harm and undermine confidence in your organisation.
Data protection is increasingly being understood not as a box-ticking exercise, but as part of responsible leadership.
What misconceptions about data protection have you spent the most time trying to correct?
One misconception is that data protection is about preventing organisations from using data. It is not. It is about ensuring that data is used lawfully, fairly, transparently and responsibly.
Another is that compliance is only relevant to large technology companies. Every organisation that processes personal data has responsibilities, whether it is a government agency, bank, school, hospital, NGO or small business.
Most importantly, data protection is not about making organisations afraid of data. It is about helping them use data responsibly while protecting the rights and dignity of the people behind that data.
Which milestone during your tenure do you believe has had the greatest impact on ordinary Kenyans and their privacy?
The establishment of a functioning complaints and enforcement mechanism.
Ordinary citizens’ rights become meaningful when there is somewhere they can turn when those rights are violated.
The ability of a data subject to raise a concern, have it investigated and, where appropriate, have an organisation held accountable has helped demonstrate that privacy is not merely an abstract constitutional or legal principle.
It has also sent an important message: personal data belongs to real people, and organisations must take responsibility for how they handle it.
How has the ODPC’s enforcement approach evolved during your tenure?
Our enforcement approach has evolved as the Office has gained experience and as the nature of data protection risks has become more complex.
Earlier, there was a strong emphasis on creating awareness and encouraging organisations to understand and comply with the new framework. As the ecosystem matured, enforcement necessarily became more prominent.
Today, we have a more established approach to investigations, determinations and corrective measures. The objective has never been enforcement for its own sake. It is about accountability, deterrence and, ultimately, better protection for data subjects.
What was the toughest enforcement decision of your tenure, and what did it teach you?
The toughest decisions are those with significant competing interests.
But that is also where the independence of a regulator is tested.
The lesson is that regulatory decisions must be grounded in evidence, the law and due process, not in the identity or influence of the organisation involved.
You cannot build public confidence in a regulator if people believe that some organisations are above accountability. Independence therefore has to be demonstrated through action, not only stated as a principle.
Looking back, is there an area where you believe the ODPC could have acted more aggressively or moved faster?
Every institution learns as it grows, and we have had to develop systems, capacity and processes while simultaneously responding to a rapidly changing technology environment.
I would distinguish between moving quickly and moving responsibly. A regulator must act with urgency, but it must also ensure that its decisions are legally sound, procedurally fair and sustainable.
The important thing is that we have continued to learn, adapt and strengthen the institution along the way.
Is Kenya’s data protection framework keeping pace with AI, biometrics and automated decision-making?
The Office has developed and published guidance on AI and emerging technologies to help navigate digital transformation.
AI, biometrics, automated decision-making and other emerging technologies create opportunities, but they also introduce new questions around transparency, fairness, accountability and individual rights.
The answer is not simply to create a new rule every time a new technology emerges. The principles of responsible data processing remain highly relevant. What we need is regulatory interpretation and guidance that can apply those principles to new technologies.
The real question is not whether we should regulate innovation. It is how we create an environment where innovation can happen responsibly, with privacy and human rights built into the design.
As Kenya accelerates digital transformation and digital public infrastructure, what safeguards are needed?
Privacy and data protection must be considered at the design stage, rather than after a system has already been deployed.
That means asking fundamental questions early: What data is being collected? Why is it necessary? Who will have access to it? How long will it be retained? What happens if the system fails or is compromised? And what mechanisms exist for individuals to exercise their rights?
We also need strong accountability, appropriate security safeguards, transparency and meaningful oversight.
Digital transformation should make people’s lives better without requiring them to surrender their fundamental rights in the process.
When you look back at the early days of the ODPC, what achievement are you most proud of?
Helping establish an institution that did not exist and seeing it become a functioning regulator that Kenyans recognise and engage with.
Building systems, processes and structures is important, but what makes me particularly proud is seeing the Office become part of the national conversation about privacy, technology and responsible data use.
When citizens know they have rights, when organisations know they have responsibilities, and when both understand that there is an institution there to provide oversight and accountability, you know that the institution has begun to fulfil its purpose.
Greatest of all is the recognition by the Global Privacy Assembly for the outstanding role of ensuring citizens’ personal data is well protected. The awards included Education and Public Awareness, Dispute Resolution and Enforcement Measures, Innovation, and the People’s Choice Award.
If you had to identify three things that define your tenure, what would they be?
I would say institution-building, accountability and awareness.
Institution-building: We were establishing a regulator from the ground up.
Accountability: Data protection rights only become meaningful when there are consequences for violations.
Awareness: A regulator cannot protect people who do not know their rights, and organisations cannot comply with obligations they do not understand.
What unfinished business are you leaving behind for your successor?
Deepening compliance across the public and private sectors, strengthening institutional capacity and keeping regulation responsive to emerging technologies.
We also need to continue improving public awareness, particularly among people who may be most vulnerable to misuse of their personal information.
The framework is in place and the institution is established, but data protection is not a destination. It is an ongoing process that has to evolve alongside technology, business models and society.
What is the one area where you believe the next Data Commissioner must be bold?
Protecting the independence and credibility of the Office.
The next Commissioner must also confront emerging risks early rather than waiting for harm to become widespread.
AI, large-scale data ecosystems, digital public infrastructure, biometrics and cross-border data flows will require strong leadership.
Boldness should always be accompanied by fairness, evidence and sound regulatory judgement. The regulator must be firm without becoming unpredictable.
What advice would you give your successor about balancing independence, enforcement, innovation and the public interest?
Protect the independence of the institution, listen widely and never lose sight of the person behind the data, the Kenyan.
Government, business and technology will continue to evolve, and the regulator has to understand those environments without losing sight of its core mandate.
Enforcement will be necessary, but so will engagement, guidance and education.
The strongest regulator is the one that creates an environment where organisations understand their responsibilities and people trust that their rights will be protected.
What do you hope people will say about the ODPC five years from now?
I hope they say the ODPC became an institution that people could trust: independent, fair, effective and responsive to the realities of a digital society.
I hope they say that Kenya became a place where innovation and privacy were not seen as competing objectives, but as things that can coexist.
I would want ordinary Kenyans to feel that their personal information is treated with dignity and that they have a meaningful voice when their privacy is threatened.
What has serving as Kenya’s inaugural Data Commissioner taught you about leadership?
It has taught me that leadership is not about having all the answers. It is about building the right team, listening, making difficult decisions when necessary and remaining accountable for those decisions.
Building an institution from the ground up also taught me the importance of patience. You can have a clear vision, but institutions take time to develop. You have to keep moving forward while understanding that sustainable change is rarely instantaneous.
And most importantly, leadership requires you to remain focused on purpose, particularly when the environment around you becomes complicated.
What has been the most difficult lesson of leading a regulator whose decisions can affect government, business and citizens?
The most difficult lesson is that regulatory decisions rarely satisfy everyone.
A decision that protects an individual’s rights may create discomfort for an organisation. A decision affecting a public institution may attract criticism from another stakeholder. Sometimes, doing what you believe is right means making a decision that will not be popular with everyone.
That taught me that leadership in regulation requires conviction, but also humility. You have to be willing to listen, explain your decisions and accept scrutiny while remaining guided by the law and the public interest.
Was there a moment during your tenure when you thought, “This is why this office matters”?
There have been many such moments, particularly when we have seen ordinary citizens come forward because they believe their personal information has been misused and expect the Office to do something about it.
Those moments bring the mandate down from policy and legislation to the individual level.
It is no longer about regulatory frameworks or institutional structures. It is about someone’s identity, dignity, livelihood or personal life.
What would you do differently if you were starting the journey again today?
I would invest earlier and more heavily in building public understanding of data protection.
We focused significantly on establishing the institutional and regulatory foundations, as we needed to, but public awareness is an area that can never be treated as secondary.
I would also place greater emphasis from the beginning on anticipating technological change. The pace of innovation has shown us that regulators cannot simply respond to yesterday’s problems. We have to be thinking about what is coming next.
But I would not change the fundamental approach of building the institution on independence, accountability and the public interest.
If you could speak to the Immaculate Kassait who walked into the ODPC in November 2020, knowing everything you know today, what would you tell her?
I would tell her: Trust the process, trust the people around you and remember why you started.
There will be difficult days. There will be criticism. There will be moments when the scale of what you are trying to build feels overwhelming.
But institutions are built one decision, one system, one person and one relationship at a time.
I would also tell her not to underestimate what it means to be “the first”. You will not have a blueprint for everything, and sometimes you will have to create the path as you walk it.
Most importantly, I would tell her to keep the citizen at the centre of the work.
Because at the heart of data protection is not technology, regulation or institutions. It is people, and their right to dignity, privacy and control over their personal information.