
advertisement
Ethiopian Airlines Breach Puts 72-Hour Data Reporting Rule Under Scrutiny

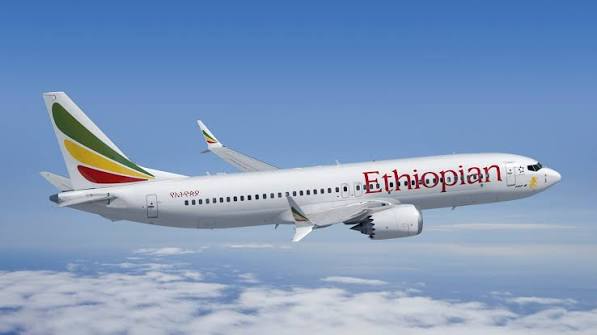
Ethiopian Airlines is investigating a cybersecurity breach affecting its ShebaMiles loyalty programme after unauthorised access to customer information triggered a notification to members on November 18.
The incident puts Ethiopia’s personal data protection requirements under scrutiny, particularly the obligation for organisations to report breaches to the regulator within 72 hours of becoming aware of them.
In a notice to customers, the airline described the incident as limited in scope and warned that certain customer information might have been affected. It said there was no evidence that financial information had been accessed.
advertisement
Chief Executive Mesfin Tasew confirmed the investigation to Reuters on November 19 but did not provide further details about the incident.
The airline has not publicly identified the categories of information involved or explained which systems were accessed. It has also not disclosed the precise date on which the intrusion began.
However, Addis Fortune reported on November 19 that fewer than 8,000 ShebaMiles accounts had been reached. The publication quoted Lemma Yadecha, Ethiopian Airlines’ Chief Commercial Officer, saying the intrusion had been contained.
advertisement
The airline detected suspicious activity on November 17 and notified members the following day, according to the report. The investigation was continuing to establish the extent of the intrusion.
ShebaMiles had more than 5.38 million members in October 2025, making the reported number of affected accounts a relatively small proportion of its membership. However, the number alone does not establish the sensitivity of the information accessed or the potential consequences for customers.
The incident comes as Ethiopia strengthens its cybersecurity and personal data protection framework.
advertisement
Proclamation No. 1321/2024, published in the Federal Negarit Gazette on July 24, 2024, requires data controllers to notify the Ethiopian Communications Authority (ECA) of a personal data breach within 72 hours of becoming aware of it.
Article 43 also requires organisations to document breaches, including their circumstances, effects and remedial measures. Data processors must notify controllers without undue delay after becoming aware of an incident.
Article 44 requires controllers to communicate breaches to affected individuals within 72 hours, subject to specified exceptions.
Ethiopian Airlines has not publicly confirmed when it notified the ECA or whether the regulator has received a formal report.
What changes for CIOs
The breach illustrates why cybersecurity incidents involving customer databases cannot be treated solely as technical problems.
For CIOs, the immediate challenge is establishing what happened, which systems were affected and whether information held by external technology providers was exposed.
Loyalty programmes contain information that can be valuable to criminals even when payment details remain untouched. Names, email addresses, account identifiers and travel histories can help attackers construct convincing phishing messages targeting customers.
Ethiopian Airlines has advised ShebaMiles members to remain alert to suspicious or unsolicited communications. This shifts part of the incident response beyond technical containment to customer protection and fraud prevention.
The incident also raises questions about the security of systems supporting airline operations. Loyalty platforms connect customer databases, booking services, marketing systems and partner programmes. Access to one environment does not automatically establish access to another, but CIOs need evidence to demonstrate where the boundaries lie.
Ethiopian Airlines uses Sabre for its passenger reservation systems, according to Addis Fortune. However, there is no evidence linking Sabre to the ShebaMiles incident.
That distinction matters when assessing supplier exposure. CIOs should avoid assuming that a breach in one customer-facing platform originated with, or affected, every connected technology provider.
The wider aviation industry has also faced scrutiny over customer information held by travel technology systems. Several international airlines have recently disclosed incidents involving booking data associated with Amadeus.
There is, however, no public evidence connecting the Ethiopian Airlines incident to Amadeus. The airline’s reservation technology and the ShebaMiles breach should therefore be treated as separate matters unless investigators establish otherwise.
For Ethiopian organisations, the regulatory implications are more immediate. The 72-hour notification requirement makes detection, escalation and legal assessment interdependent. A security team that identifies suspicious activity but delays notifying legal and privacy officers can leave the organisation with little time to establish the facts and meet its obligations.